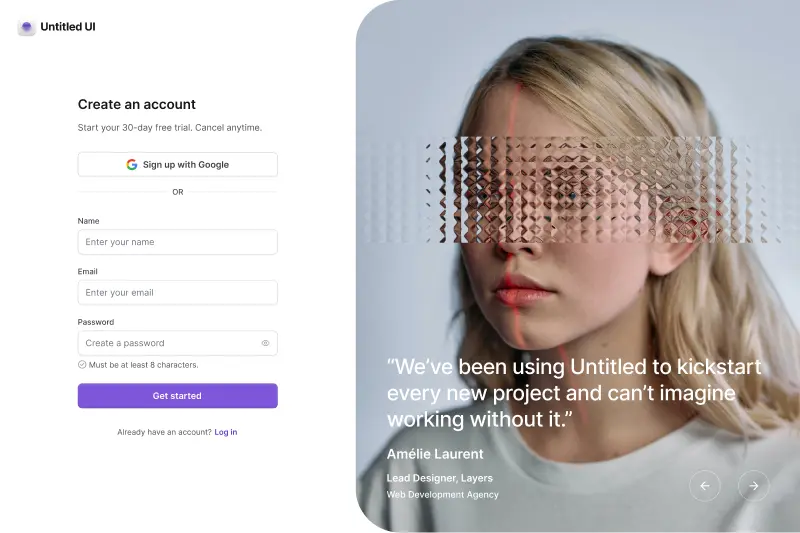



Figma forgot password page header examples


Forgot password page headers in Figma: steps, states, and copy
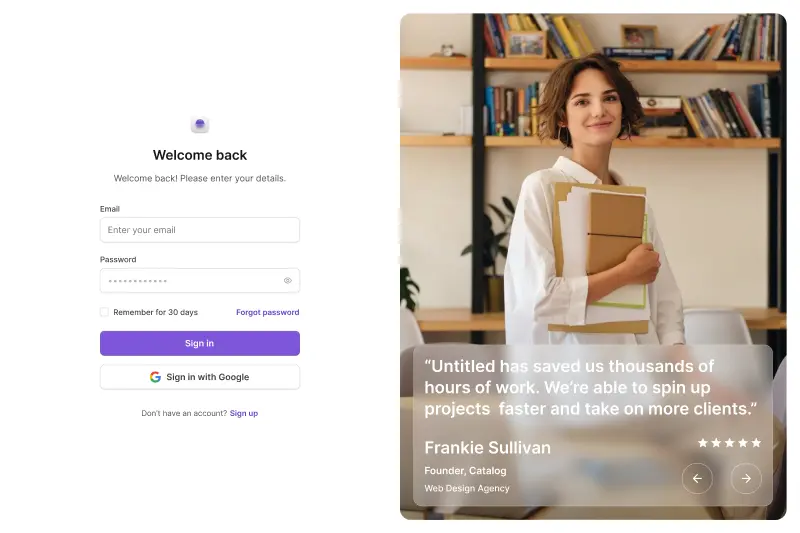
Password reset is a rescue operation. Nobody arrives here on purpose, everybody arriving is already mildly annoyed, and the flow has to work on a phone, in a hurry, with an inbox in the way.
That is a strong argument for making it the least decorated corner of your product. Four screens do the whole job, and this set draws each of them at both breakpoints.
Four steps under one property
The component set has a single property, Step, with values for forgot password, check email, set new password, and success, plus a sidebar version that reframes the same flow with a panel down one side. Each is drawn at 1,440px by 960px on desktop and 375px by 812px on mobile, and the whole set is duplicated in dark.
Keeping the four as variants rather than four loose frames matters more here than it sounds. The reset flow is the one designers copy between projects, and a variant set travels intact while a folder of frames arrives with the success screen missing.
Step 1 should not tell you whether the account exists
The first screen asks for an email address, and the reply is where teams leak information without noticing. "No account with that address" is friendly, and it hands anyone holding a list of emails a way to find out who uses your product.
The safer wording, and the one this layout is built around, is a confirmation that confirms nothing: if an account exists for that address, a link is on its way. Slightly worse for the honest user who mistyped, considerably better for everyone whose membership of your service is nobody else's business.
Reuse the same check-your-email screen your verification flow uses, so people who have seen one recognise the other.
Setting the new password
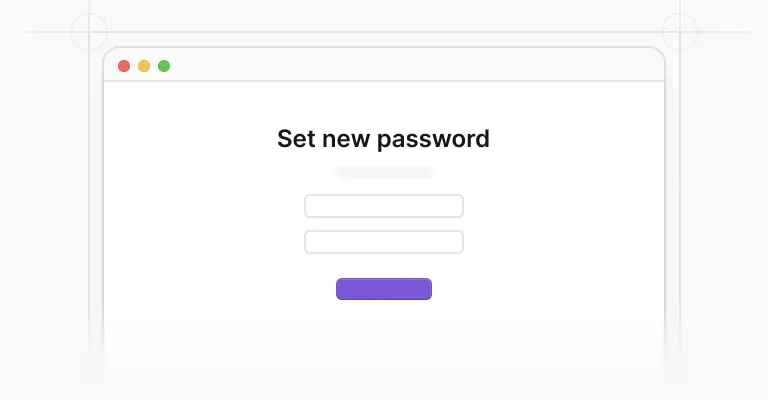
Step 3 decides whether the reset finishes. Show the rules before anyone types instead of after they fail, offer a visibility toggle, and prefer a strength meter to a list of rejections, all of which Nielsen Norman Group's password creation research argues for directly.
Then look hard at the rules themselves. NIST's guidance advises against forcing mixtures of character types and puts the minimum at eight characters, which means many of the symbol requirements still in production are making passwords harder to remember without making them harder to crack.
Blocking paste is worse again: it defeats password managers, and WCAG 2.2's accessible authentication criterion counts it as a conformance failure. The input components supply the helper and error text these screens hang the rules on.
The success screen has a job
Step 4 is not a formality. It confirms the password changed, which is the thing the person actually wanted to know, and it is the natural place to send them back to log in or, better, into the product already signed in.
Two details are worth adding beyond the layout: say that other sessions have been signed out if they have, and send a separate notification email about the change, since an unexpected reset confirmation is how people find out their account is under attack.
The email templates cover that message, and getting it visually consistent with the reset screens is what stops it looking like the phishing attempt it is warning about.
When it is time to build, the same screens exist in code. Untitled UI React forgot password pages are open source, built with Tailwind CSS and React Aria, with the field states and step transitions handled for you.
Frequently asked questions
Should a password reset page say when an email address has no account?
No. Confirming which addresses have accounts turns your reset form into a lookup tool for anyone with a leaked email list, and for some products the membership itself is sensitive information.
Use one neutral response for every address: if an account exists, a link is on the way. Someone who mistyped will work it out when nothing arrives, which is a small price against handing out account existence to anyone who asks.
Should the new password be entered twice for confirmation?
One field with a visibility toggle beats two fields. Asking people to type the same string twice while it is masked is a way of catching typos that produces its own typos, then a mismatch error at the end of an already irritating flow.
Let them read what they typed instead. If policy forces the confirm field on you, at least validate it as they type rather than on submit.
How long should a password reset link stay valid?
Short. An hour is generous for a link sent in response to a request the person just made, and single use matters more than the duration: the link should stop working the moment the password changes or a newer link is issued.
Whatever you pick, an expired link needs its own screen with a resend button on it rather than a generic error.
Are these forgot password headers included in the free version?
The password reset screens are part of the paid Untitled UI Figma kit, and pricing covers what comes with it.
The 100% free Figma UI kit includes core components from the same system if you want to try it before buying.
Is there a React version of these forgot password pages?
Yes. Untitled UI React forgot password pages are open source, built with Tailwind CSS and React Aria, and mirror these Figma screens through all four steps.
Foundation Figma components and styles
Figma base components
Shared Figma assets
Application UI/Dashboard examples
Application UI/Dashboard Figma components
Marketing website examples
What is Untitled UI?


Untitled UI is the best $ I've spent on my business in a long time. I'm going to keep using it and recommending it to every designer I know.

Over the years we've featured hundreds of UI kits on UXCrush, but Untitled UI is by far the most comprehensive and detailed I've seen yet. A must have for any designer!
I've used all UI kits on the market. I can say without a doubt that the Untitled UI kit is the best on the market. It covers everything a designer needs in a modern and efficient way.

Incredible, and keeps getting better. I’ve tried dozens of UI kits and Untitled UI is the only name you should care about. It stands head and shoulders above the rest.
Such a beautiful, detailed, and extensive UI kit. Untitled UI is the perfect foundation for any project. I highly recommend this huge time saver.
Untitled UI has been an amazing resource that I'm learning to rely upon to spin up ideas in no time. I think I might launch a startup pretty soon by mistake here!
The sheer scale, details, and organization of this kit is mind-blowing. It covers nearly everything a Designer could need in a modern, efficient and systematic way.
I'm super impressed with this. I love poking around in other peoples UI Kits to see how they think. This is probably one of the most comprehensive I've seen.
I'm super excited to use this for quick mockups of ideas in Figma. We're always trying to streamline our design process so we can move fast! Definitely recommend.
Untitled UI is easily the best UI kit I've used so far. It has an insane amount of components that are all incredibly well-built. I don't even know how many hours this will save.

The attention to detail and thought Jordan has put into this UI kit is unparalleled.
Untitled UI is incredibly well-organized and the attention to detail is great. I highly recommend this kit to any designer that wants to create beautiful designs fast.
What an awesome Figma kit... it's an absolute game changer. This is the perfect base for any design system. The size and attention to detail is next level.
We've been using Untitled to build Himalayas 2.0 and have finished a complete redesign in just a few days. It has everything we need already pixel-perfect.